Qualys Vulnerability Management
Vulnerability Management- Overview
- Setup
- Data & mappings
- Operations & API
- Changelog
The Qualys Vulnerability Management Connector fetches host asset and vulnerability detection data from the Qualys VM platform. It connects to the Qualys VM API to synchronize hosts, vulnerability detections, and knowledge base entries, mapping them to the Brinqa Data Model.
Data retrieved from Qualys Vulnerability Management
| Connector Object | Required | Maps to Data Model |
|---|---|---|
| Host | Yes | Host |
| Vulnerability | Yes | Vulnerability |
| Vulnerability Definition | Yes | Vulnerability Definition |
Model relationships
For detailed steps on how to view the data retrieved from Qualys Vulnerability Management in the Brinqa Platform, see How to view your data.
Note: Qualys excludes hosts whose vulnerability-processed date is null from vm_processed_* filters. Since delta syncs scope the host listing with vm_processed_after, a host that has never had vulnerability data processed is not listed by a delta and is picked up only by a full sync.
Connection settings
When setting up a data integration, select Qualys Vulnerability Management from the Connector dropdown and provide the following:
| Setting | Required | Default | Description |
|---|---|---|---|
| API Server URL | Yes | https://qualysapi.qualys.com/ | Qualys platform API server url |
| Username | Yes | — | Qualys user login |
| Password | Yes | — | Qualys user password |
| Page size | No | 100 | Maximum number of hosts to request per API request |
| Parallel requests | No | 2 (or available processors) | Maximum number of parallel API requests |
| Maximum retries | No | 5 | The maximum number of retry attempts before giving up a request |
| Request timeout (secs) | No | 120 | The maximum seconds allotted before a request will time out. Enter zero (0) to disable timeouts (not recommended). |
Authentication
The connector authenticates with the Qualys API using HTTP Basic Authentication (username and password). Credentials are supplied through the connector configuration and sent on every request — there is no token or session exchange.
Usage
All API requests include the Basic Auth credentials:
Authorization: Basic <base64(username:password)>
Sync Behavior
The connector performs incremental (delta) syncs. Brinqa passes a sync token carrying the timestamp of the previous successful sync (since):
- First sync (no token): a full sync is performed — all records are retrieved.
- Subsequent syncs: the
sincetimestamp is applied as a server-side filter so that only records changed after the previous sync are returned:- Host filters by the
vm_processed_after=<since>query parameter. - Vulnerability filters detections by
detection_updated_since=<since>, and scopes its host-ID listing byvm_processed_after=<since>exactly as the Host sync does. - Vulnerability Definition filters by the
last_modified_after=<since>query parameter (WAS-only knowledge base entries are excluded after fetch).
- Host filters by the
Both the Host and Vulnerability syncs begin by enumerating host IDs from the Qualys host API, scoped on a delta so only the hosts Qualys processed since the previous run are listed. To avoid fetching the same list twice, the enumeration is cached to a local, transaction-scoped store: the Host sync populates it and the Vulnerability sync reuses it — but only when the stored list actually covers what that sync needs. The two models keep their own sync positions, so the Vulnerability sync can be further behind than the Host sync; when the stored list was built for a shorter window, or with different host filters (asset groups, tags, networks), it is re-enumerated rather than inherited, so a narrower host set is never mistaken for a complete one. Each host-ID page is written to the store and handed to detail fetching as it arrives, so caching does not delay records. The store lives under the OS temp directory, is keyed by transaction ID, and is cleaned up automatically once the sync completes (stale directories from interrupted syncs are pruned after a day).
How to obtain Qualys Vulnerability Management credentials
Create a Qualys user
To ensure the user account that the Qualys VM connector uses to access the Qualys server has the appropriate permissions, follow these steps.
-
Log in to your organization's Qualys server.
-
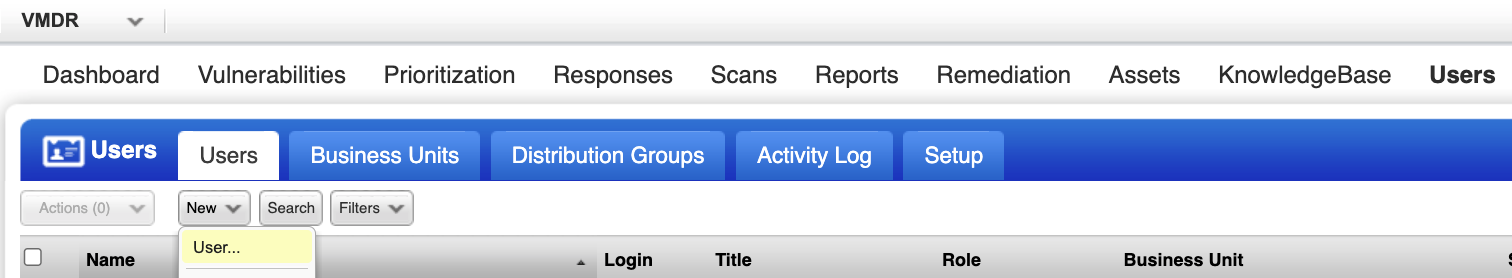
Navigate to Users, and then select the Users tab.
-
Click New and select User. The New User dialog displays.
-
Fill out the general information for the new user.
-
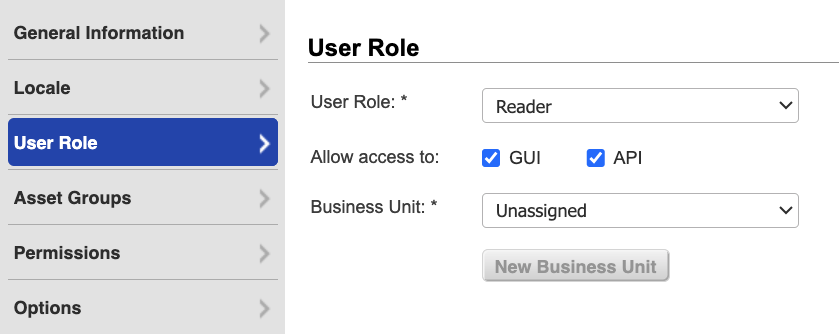
Click User Role on the left menu.
-
From the User Role dropdown, select Reader.
-
Select GUI and API to enable API access, and leave Business Unit Unassigned.
-
Note: GUI access allows the user to log in to the Qualys GUI (graphical user interface). After you create the new Qualys user, log in to the Qualys GUI using the new credentials. The system prompts the user to reset their password. The Qualys connector will not function until you complete the password reset.
-
Click Asset Groups.
- From the Add asset groups dropdown, select All or only the asset groups the Qualys user needs access to.
-
Click Permissions and select all of the available permissions.
-
Click Options to modify the notification options as needed.
-
Click Save.
The new Qualys user with appropriate permissions to retrieve data displays on the Qualys Users page.
If you do not wish to create a new Qualys user, you can leverage an existing user with the appropriate permissions.
Note: If you do not have permissions to create a new Qualys user, contact your Qualys administrator. For additional information, see Qualys documentation.
Enable CVSS scoring in Qualys
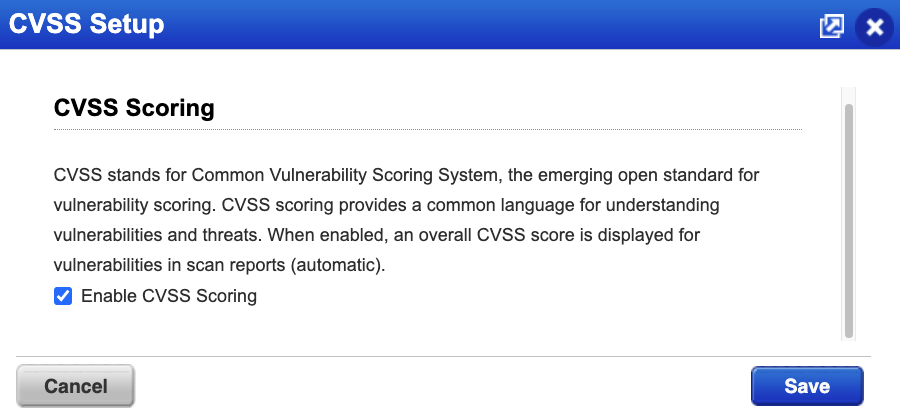
To ensure that the Qualys VM connector accurately retrieves CVSS scoring information, including Temporal Scores, from your Qualys environment, you must enable a specific setting in Qualys. This setting is not enabled by default. To enable this setting, follow these steps:
-
Log in to your organization's Qualys server.
-
Navigate to Vulnerability Management > Reports.
-
Click the Setup tab and then click CVSS.
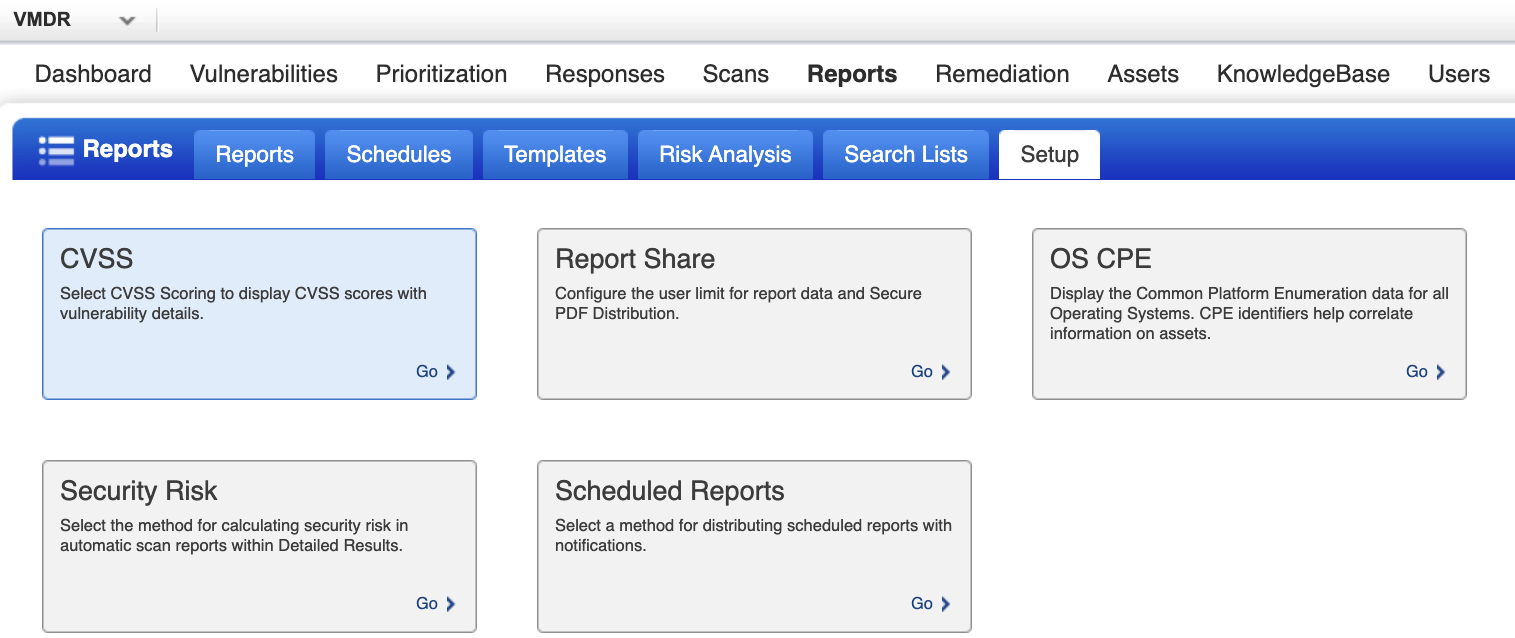
The CVSS Setup window displays.
-
Click Enable CVSS Scoring and then click Save.
Attribute mappings
Expand the sections below to view the mappings between the source and the Brinqa data model attributes:
Host
| Source Field Name | SDM Attribute |
|---|---|
All DNS names (combined) | DNS_NAMES |
All IP addresses (combined) | IP_ADDRESSES |
| ASSET_CATEGORY_HOST, ASSET_CATEGORY_VIRTUAL_MACHINE | CATEGORIES |
| Azure ipv6 | AZURE_IPV6 |
| Azure location | AZURE_LOCATION |
| Azure mac | AZURE_MAC_ADDRESS |
| Azure name | AZURE_NAME |
| Azure osType | AZURE_OS_TYPE |
| Azure privateIp | AZURE_PRIVATE_IPV4 |
| Azure public-ipv4 | AZURE_PUBLIC_IPV4 |
| Azure resourceGroupName | AZURE_RESOURCE_GROUP_NAME |
| Azure state | AZURE_STATE |
| Azure subnet | AZURE_SUBNET |
| Azure subscriptionId | AZURE_SUBSCRIPTION |
| Azure vmId | AZURE_VM_ID |
| Cloud metadata name / DNS hostname / NetBIOS / IP | NAME |
Cloud metadata state (normalized) or "active" | STATUS |
| EC2 accountId | EC2_AWS_ACCOUNT |
| EC2 availabilityZone | EC2_AVAILABILITY_ZONE |
| EC2 hostname | EC2_HOSTNAME |
| EC2 imageId | EC2_AMI_ID |
| EC2 instanceId / instance-id | EC2_INSTANCE_ID |
| EC2 instanceState | EC2_INSTANCE_STATE |
| EC2 instanceType / instance-type | EC2_INSTANCE_TYPE |
| EC2 local-ipv4 / privateIp | EC2_PRIVATE_IPV4 |
| EC2 mac | EC2_MAC_ADDRESS |
| EC2 public-ipv4 | EC2_PUBLIC_IPV4 |
| EC2 region | EC2_REGION |
| EC2 security-groups | EC2_SECURITY_GROUPS |
| EC2/Azure/GCP mac attribute | MAC_ADDRESSES |
| GCP hostname | GCP_HOSTNAME |
| GCP instance-id | GCP_INSTANCE_ID |
| GCP mac | GCP_MAC_ADDRESS |
| GCP machineType | GCP_MACHINE_TYPE |
| GCP network | GCP_NETWORK |
| GCP privateIp | GCP_PRIVATE_IPV4 |
| GCP projectId | GCP_PROJECT_ID |
| GCP public-ipv4 | GCP_PUBLIC_IPV4 |
| GCP state | GCP_STATE |
| GCP zone | GCP_ZONE |
host.getAGENTACTIVATIONKEY | AGENT_ACTIVATION_KEY |
host.getAGENTACTIVATIONTITLE | AGENT_ACTIVATION_TITLE |
host.getAGENTSTATUS | AGENT_STATUS |
host.getARSFACTORS.getARSFORMULA | ARS_FORMULA |
host.getASSETCRITICALITYSCORE | ACS |
host.getASSETID | ASSET_ID |
host.getASSETRISKSCORE | ARS |
host.getCLOUDAGENTRUNNINGON | CLOUD_AGENT_RUNNING_ON |
host.getCLOUDPROVIDER | CLOUD_PROVIDER |
host.getCLOUDPROVIDERTAGS | CLOUD_PROVIDER_TAGS |
host.getCLOUDRESOURCEID | CLOUD_RESOURCE_ID |
host.getCLOUDRESOURCEID, EC2/Azure/GCP metadata | INSTANCE_ID |
host.getCLOUDSERVICE | CLOUD_SERVICE |
host.getDNSDATA.getDOMAIN | DOMAIN |
host.getDNSDATA.getFQDN (private) | PRIVATE_DNS_NAMES |
host.getDNSDATA.getFQDN (public) | PUBLIC_DNS_NAMES |
host.getDNSDATA.getHOSTNAME | DNS_HOSTNAME |
host.getFIRSTFOUNDDATE / EC2/GCP firstDiscovered | FIRST_SEEN |
host.getHARDWAREUUID | HARDWARE_ID |
host.getID | UID |
host.getIP (private), EC2/Azure/GCP privateIp | PRIVATE_IP_ADDRESSES |
host.getIP (public), EC2/Azure/GCP public-ipv4 | PUBLIC_IP_ADDRESSES |
host.getLASTACTIVITY | LAST_ACTIVITY |
host.getLASTBOOT | LAST_STARTED |
host.getLASTVMAUTHSCANNEDDATE | LAST_AUTH_SCANNED |
host.getLASTVULNSCANDATETIME | LAST_SCANNED |
host.getNETBIOS | NETBIOS_HOSTNAME |
host.getNETBIOS, host.getDNSDATA.getHOSTNAME, host.getOSHOSTNAME | HOSTNAMES |
host.getNETWORKID | NETWORK_ID |
host.getOS | OPERATING_SYSTEM |
host.getOSHOSTNAME | OS_HOSTNAME |
host.getOWNER | OWNER |
host.getQGHOSTID | QG_HOST_ID |
host.getSERIALNUMBER | SERIAL_NUMBER |
host.getTAGS.getTAG | TAGS |
host.getTRACKINGMETHOD | TRACKING_METHOD |
host.getTRURISKSCORE | TRURISK_SCORE |
host.getTRURISKSCOREFACTORS.getTRURISKSCOREFORMULA | TRURISK_SCORE_FORMULA |
Instant.now() at sync start | LAST_CAPTURED |
| Latest of LAST_SCANNED or LAST_ACTIVITY | LAST_SEEN |
| name + OS | DESCRIPTION |
Vulnerability
| Source Field Name | SDM Attribute |
|---|---|
| Calculated from severity | SEVERITY_SCORE |
| Calculated from status | STATUS_CATEGORY |
detection.getAFFECTEXPLOITABLECONFIG | AFFECTS_EXPLOITABLE_CONFIG |
detection.getAFFECTRUNNINGKERNEL | AFFECTS_RUNNING_KERNEL |
detection.getAFFECTRUNNINGSERVICE | AFFECTS_RUNNING_SERVICE |
detection.getFIRSTFOUNDDATETIME | FIRST_FOUND |
detection.getFIRSTREOPENEDDATETIME | FIRST_REOPENED |
detection.getISDISABLED | IS_DISABLED |
detection.getISIGNORED | IS_IGNORED |
detection.getLASTFIXEDDATETIME | LAST_FIXED |
detection.getLASTFOUNDDATETIME | LAST_FOUND |
detection.getLASTPROCESSEDDATETIME | LAST_PROCESSED |
detection.getLASTREOPENEDDATETIME | LAST_REOPENED |
detection.getLASTTESTDATETIME | LAST_SCANNED |
detection.getLASTUPDATEDATETIME | SOURCE_LAST_MODIFIED |
detection.getLATESTVULNERABILITYDETECTIONSOURCE | LATEST_VULNERABILITY_DETECTION_SOURCE |
detection.getPORT | PORT |
detection.getPROTOCOL | PROTOCOL |
detection.getQDS.severity | QDS_SEVERITY |
detection.getQDS.value | QDS_SCORE |
detection.getQDSFACTORS | QDS_FACTORS |
detection.getQID | QID |
detection.getRESULTS | RESULTS |
detection.getSERVICE | SERVICE |
detection.getSEVERITY | SOURCE_SEVERITY |
detection.getSEVERITY (as double) | SOURCE_SEVERITY_SCORE |
detection.getSEVERITY (normalized) | SEVERITY |
detection.getSSL | SSL |
detection.getSTATUS | PROVIDER_STATUS |
detection.getSTATUS (normalized) | SOURCE_STATUS |
detection.getSTATUS (normalized) | STATUS |
detection.getTIMESFOUND | TIMES_FOUND |
detection.getTIMESREOPENED | TIMES_REOPENED |
detection.getTYPE | DETECTION_TYPE |
detection.getUNIQUEVULNID | UNIQUE_VULN_ID |
detection.getUNIQUEVULNID or MD5(hostId, qid, port, protocol, service) | UID |
detection.getVULNERABILITYDETECTIONSOURCES | VULNERABILITY_DETECTION_SOURCES |
host (private DNS names) | PRIVATE_DNS_NAMES |
host.getDNS | PUBLIC_DNS_NAMES |
host.getID | TARGETS |
host.getID | HOST_ID |
host.getIP | IP_ADDRESSES |
host.getNETBIOS | HOSTNAMES |
host.getQGHOSTID | QG_HOST_ID |
host.getTAGS.getTAG (names) | TAGS |
Instant.now() at sync start | LAST_CAPTURED |
QID_PREFIX + detection.getQID | TYPE |
Vulnerability Definition
| Source Field Name | SDM Attribute |
|---|---|
| Calculated from severity | SEVERITY_SCORE |
discovery.getAUTHTYPELIST | Auth type |
discovery.getREMOTE | Discovery |
Instant.now() at sync start | LAST_CAPTURED |
QID_PREFIX + vuln.getQID | UID |
vuln.getAUTOMATICPCIFAIL | Automatic PCI failure |
vuln.getBUGTRAQLIST | BugTraq ID |
vuln.getCATEGORY | CATEGORIES |
vuln.getCOMPLIANCELIST | Compliance type |
vuln.getCONSEQUENCE | SUMMARY |
vuln.getCORRELATION (exploits) | EXPLOITS |
vuln.getCORRELATION (malware) | MALWARE |
vuln.getCVELIST | CVE_IDS |
vuln.getCVELIST | CVE_RECORDS |
vuln.getCVSS.getBASE | CVSS_V2_BASE_SCORE |
vuln.getCVSS.getTEMPORAL | CVSS_V2_TEMPORAL_SCORE |
vuln.getCVSS.getVECTORSTRING / vuln.getCVSSV3.getVECTORSTRING / vuln.getCVSSV4.getVECTORSTRING | CVSS Metrics |
vuln.getCVSSV3.getBASE | CVSS_V3_BASE_SCORE |
vuln.getCVSSV3.getTEMPORAL | CVSS_V3_TEMPORAL_SCORE |
vuln.getCVSSV4.getBASE | CVSS_V4_BASE_SCORE |
vuln.getDIAGNOSIS | DESCRIPTION |
vuln.getLASTSERVICEMODIFICATIONDATETIME | SOURCE_LAST_MODIFIED |
vuln.getPATCHABLE | PATCHABLE |
vuln.getPCIFLAG | PCI flag |
vuln.getPCIREASONS | PCI reasons |
vuln.getPUBLISHEDDATETIME | PUBLISHED_DATE |
vuln.getSEVERITYLEVEL (as double) | SOURCE_SEVERITY_SCORE |
vuln.getSEVERITYLEVEL (normalized) | SEVERITY |
vuln.getSOFTWARELIST (products) | AFFECTED |
vuln.getSOFTWARELIST (vendors) | Vendor |
vuln.getSOLUTION | RECOMMENDATION |
vuln.getTHREATINTELLIGENCE | Threat indicators |
vuln.getTITLE | NAME |
vuln.getVENDORREFERENCELIST (URLs) | REFERENCES |
vuln.getVULNTYPE | Type |
Operations & API
Expand each connector object to see its operation options, delta-sync behavior, and the API it uses. See connector operation options for how to apply operation options (keys and values are case-sensitive).
Host
Operation options
| Option | Type | Default | Description |
|---|---|---|---|
ips | String | — | Filter by IP address or range |
ids | String | — | Filter by specific host IDs |
id_min | String | — | Minimum host ID |
id_max | String | — | Maximum host ID |
ag_ids | String | — | Filter by asset group IDs |
ag_titles | String | — | Filter by asset group names |
network_ids | String | — | Filter by network IDs |
os_pattern | String | — | Filter by OS pattern (regex) |
os_hostname | String | — | Filter by hostname pattern |
host_metadata | String | all | Cloud metadata provider (all, ec2, google, azure) |
host_metadata_fields | String | — | Specific metadata fields to retrieve |
use_tags | String | — | Enable tag-based host filtering (1) |
tag_set_by | String | — | Reference tags by name or id |
tag_set_include | String | — | Only sync hosts matching these tag names |
tag_set_exclude | String | — | Exclude hosts matching these tag names |
tag_include_selector | String | — | Tag include selector logic (any, all) |
tag_exclude_selector | String | — | Tag exclude selector logic (any, all) |
ars_min | String | — | Minimum Asset Risk Score |
ars_max | String | — | Maximum Asset Risk Score |
show_ars | String | — | Include ARS data in response (0, 1) |
show_ars_factors | String | — | Include ARS factor breakdown (0, 1) |
hostListPageSize | Number | 10000 | Host IDs per host-list page (truncation_limit); 0 returns every ID in one response. A value below pageSize is raised to pageSize, since a page too small to fill one detail batch would leave parallel requests idle; an invalid (negative) value falls back to the default |
deltaLookbackMinutes | Number | 60 | Minutes of overlap subtracted from since before it is sent as a source-side filter (vm_processed_after on the host listing, detection_updated_since on the detection request), so a record stamped either side of the previous run's boundary is not missed. 0 filters on since verbatim; an invalid (negative) value falls back to the default |
Delta sync
Supported. The connector performs an incremental (delta) sync via the since sync token, filtering on vm_processed_after.
API
- Type: REST (classic Qualys VM XML API; XML response parsed via JAXB) · Endpoint:
POST /api/4.0/fo/asset/host/ - Default filters:
show_tags=1,show_asset_id=1,show_cloud_tags=1,show_trurisk=1,show_trurisk_factors=1,cloud_agent_activationkey=1, andhost_metadata=allare sent by default on the phase 2 detail fetch. On delta syncsvm_processed_afteris applied to the phase 1 enumeration, so only the hosts Qualys processed since the previous run are listed; phase 2 then names those IDs explicitly and needs no filter of its own.
Vulnerability
Operation options
| Option | Type | Default | Description |
|---|---|---|---|
status | String | New,Fixed,Active,Re-Opened | Detection status filter (New, Active, Re-Opened, Fixed) |
severities | String | — | Severity filter (1–5) |
qids | String | — | Filter by specific QIDs |
detection_updated_since | String | — | Override delta sync timestamp |
deltaLookbackMinutes | Number | 60 | Minutes of overlap subtracted from since before it is sent as a source-side filter (vm_processed_after on the host listing, detection_updated_since on the detection request), so a record stamped either side of the previous run's boundary is not missed. 0 filters on since verbatim; an invalid (negative) value falls back to the default |
show_reopened_info | String | 1 | Include reopened information (0, 1) |
show_results | String | — | Include detection results (0, 1) |
show_igs | String | — | Include ignored detections (0, 1) |
active_kernels_only | String | — | Active kernels only (0, 1) |
include_ignored | String | — | Include ignored detections (0, 1) |
include_disabled | String | — | Include disabled detections (0, 1) |
filter_superseded_qids | String | — | Filter superseded QIDs (0, 1) |
include_search_list_titles | String | — | Include detections from named search lists |
exclude_search_list_titles | String | — | Exclude detections from named search lists |
include_search_list_ids | String | — | Include by search list ID |
exclude_search_list_ids | String | — | Exclude by search list ID |
vuln_detection_source | String | — | Include vulnerability detection source (0, 1) |
show_qds | String | — | Include QDS data (0, 1) |
show_qds_factors | String | — | Include QDS factors (0, 1) |
qds_min | String | — | Minimum QDS score |
qds_max | String | — | Maximum QDS score |
Option | Type | Default | Description |
:--------------------- | :-------- | :-------- | :------------------------------------------------------------------------------------------------------------------- |
arf_filter | Boolean | false | Enable ARF kernel/service/config filters |
arf_kernel_filter | String | 0 | ARF kernel filter level (0–5). Requires arf_filter = true |
arf_service_filter | String | 0 | ARF service filter level (0–5). Requires arf_filter = true |
arf_config_filter | String | 0 | ARF config filter level (0–5). Requires arf_filter = true |
arf_key | Boolean | false | Enable ARF filter keys |
arf_filter_keys | String | — | ARF filter keys (non-running-kernel, non-running-service, config-not-exploitable). Requires arf_key = true |
show_arf_data | String | — | Show ARF data (0, 1). Requires arf_key = true |
Option | Type | Default | Description |
:----------------------- | :------- | :-------- | :------------------------------------------------- |
ips | String | — | Filter by IP address or range |
ids | String | — | Filter by specific host IDs |
id_min | String | — | Minimum host ID |
id_max | String | — | Maximum host ID |
ag_ids | String | — | Filter by asset group IDs |
ag_titles | String | — | Filter by asset group names |
network_ids | String | — | Filter by network IDs |
os_pattern | String | — | Filter by OS pattern (regex) |
os_hostname | String | — | Filter by hostname pattern |
use_tags | String | — | Enable tag-based host scoping (1) |
tag_set_by | String | — | Reference tags by name or id |
tag_set_include | String | — | Only sync detections for hosts matching this tag |
tag_set_exclude | String | — | Exclude detections for hosts matching this tag |
tag_include_selector | String | — | Tag include selector logic (any, all) |
tag_exclude_selector | String | — | Tag exclude selector logic (any, all) |
ars_min | String | — | Minimum Asset Risk Score |
ars_max | String | — | Maximum Asset Risk Score |
show_ars | String | — | Include ARS data (0, 1) |
show_ars_factors | String | — | Include ARS factor breakdown (0, 1) |
hostListPageSize | Number | 10000 | Host IDs per host-list page (truncation_limit) used to enumerate the hosts whose detections are fetched; 0 returns every ID in one response. A value below pageSize is raised to pageSize, since a page too small to fill one detection batch would leave parallel requests idle; an invalid (negative) value falls back to the default |
Delta sync
Supported. The connector performs an incremental (delta) sync via the since sync token, filtering on detection_updated_since.
API
- Type: REST (classic Qualys VM XML API; XML response parsed via JAXB) · Endpoint:
POST /api/4.0/fo/asset/host/vm/detection/ - Default filters:
output_format=XML,action=list,show_tags=1,show_reopened_info=1, andstatus=New,Fixed,Active,Re-Openedare sent by default. On delta syncs,detection_updated_sincescopes results to detections updated after the sync timestamp.
Vulnerability Definition
Operation options
This object does not support any operation options.
Delta sync
Supported. The connector performs an incremental (delta) sync via the since sync token, filtering on last_modified_after.
API
- Type: REST (classic Qualys VM XML API; XML response parsed via JAXB) · Endpoint:
GET /api/4.0/fo/knowledge_base/vuln/ - Default filters:
action=list,details=All,show_supported_modules_info=1. On delta syncs,last_modified_afterscopes results to KB entries modified after the sync timestamp. Entries supporting only the WAS module are excluded after fetch.
Changelog
The Qualys Vulnerability Management connector has undergone the following changes:
| Version | Description | Migration Steps |
|---|---|---|
| 5.3.49 | Improvements - Vulnerability synchronization requests detections for the hosts that changed, rather than searching the whole subscription for them. An incremental sync now lists only the hosts Qualys processed since the previous run, reuses that list for the detection requests, and names those hosts on each request so Qualys answers it by looking them up directly. On a large subscription an unnamed, subscription-wide search could take longer to answer than the request timeout allowed, which left a sync running for hours and returning nothing; a request that names its hosts does not have that failure mode. Records and their content are unchanged. - The vulnerability sync reuses the host list only when it covers the window that sync needs. The two syncs keep their own positions, so the vulnerability sync can be further behind than the host sync — after it has been disabled or failing, for example. It now re-lists the hosts for its own window in that case rather than inheriting the host sync's shorter one, which would have quietly skipped everything that changed in between and still recorded the run as complete. This supersedes the note in 5.3.48 that the two syncs always consider the same set of hosts. - Host synchronization scopes its host-ID listing by vm_processed_after, so an incremental sync lists only the hosts processed since the previous run rather than the whole subscription. Previously the filter was applied when fetching host detail, after every host in the subscription had already been listed and batched, so an incremental sync cost nearly as much as a full one. The vulnerability sync reuses this same list, so both benefit. - Host and vulnerability synchronization report the step they are running and the totals they finished with. Each sync logs the filters it is actually sending when it starts — the delta timestamp, the detection statuses, and the page sizes — so a sync that returns nothing can be explained without changing the log configuration. It then logs the number of host IDs it enumerated, and closes with the host and batch counts and the elapsed time. The closing line is written even when a sync fails partway, so a run that did not finish still records how far it reached. Bug Fixes - Fixed host ID ranges being ignored when listing hosts. Qualys returns a range wherever host IDs run contiguously, and the connector read only individually listed IDs, so every host covered by a range was skipped — no host record, and no vulnerabilities for it. A page that listed nothing but ranges produced nothing at all and the sync still completed successfully. Ranges are now expanded, and a page whose IDs cannot be read is reported rather than treated as an empty page. - Fixed vulnerability detections and host records updated close to a sync boundary being missed. An incremental sync filtered from the previous sync's timestamp exactly, so a record the source stamped within moments of that instant could fall between two runs and never be synced. Incremental syncs now re-request a short overlap window — one hour by default, adjustable with the deltaLookbackMinutes sync option, or 0 to restore the previous exact-boundary behavior. | N/A |
| 5.3.48 | Improvements - Host and vulnerability synchronization now share a single, transaction-scoped fetch of host IDs. During a sync, the host IDs retrieved for the host sync are cached to a local store and reused by the vulnerability sync, eliminating a redundant round of host-listing calls to the Qualys API and reducing overall sync time. Records continue to stream as introduced in 5.3.47: each host-ID page is cached and handed to detail fetching as it arrives, so caching for reuse does not delay the first record or grow peak memory with the host inventory. The cache is scoped to the sync transaction and cleaned up automatically. Delta scoping is unchanged in effect: host records are still scoped by vm_processed_after=<since> (now applied on the host detail fetch rather than on host-ID enumeration), and vulnerability records are still scoped by detection_updated_since=<since> on the detection fetch. Because the shared host-ID enumeration is no longer filtered, a vulnerability sync considers the same set of records whether it reuses the host sync's IDs or enumerates them itself. | N/A |
| 5.3.47 | Improvements - Vulnerability and Host syncs now start retrieving records while the host inventory is still being enumerated. Previously every matching host ID was collected in one unbounded request before the first vulnerability or host record was retrieved, which on large subscriptions left a sync producing nothing for hours. Host IDs are now requested in pages and each page's data is fetched as the page arrives, so records begin flowing shortly after the sync starts and peak memory no longer grows with the size of the host inventory. The page size defaults to 10,000 host IDs and can be adjusted with the hostListPageSize sync option; a value below the configured page size is raised to it, and 0 restores the previous single-request enumeration. | N/A |
| 5.3.46 | No changes in this release. | N/A |
| 5.3.45 | New Features - Vulnerability Definition records now capture CVSS v4.0 scoring — base score, severity, vector string, and the individual vector metrics — whenever Qualys provides it. Improvements - Vulnerability Definitions are now retrieved from the Qualys 4.0 KnowledgeBase API, ahead of Qualys ending support for the 3.0 endpoint. Existing data is unchanged. | N/A |
| 5.3.44 | No changes in this release. | N/A |
| 5.3.43 | No changes in this release. | N/A |
| 5.3.42 | No changes in this release. | N/A |
| 5.3.41 | Improvements - Added a "Last captured" timestamp to Host, Vulnerability, and Vulnerability Definition records, recording when each record was last retrieved from Qualys during a sync. Bug Fixes - Fixed an issue where parallel host and vulnerability synchronization could exceed the configured parallelism level, opening more concurrent requests to the Qualys API than intended. Parallel execution now strictly respects the configured parallelism cap. | N/A |
| 5.3.40 | Improvements - Added comprehensive MockWebServer-based integration tests to validate connection, schema, and sync workflows. This includes offline test coverage for vulnerability correlation null-safety, reproducing and verifying the fix for the NullPointerException that affected versions prior to v5.3.30. | N/A |
| 5.3.39 | Bug Fixes - Corrected host/asset date attributes ("Last boot", "OS GA date", "OS EOL date", "OS EOS date", "Whois creation date") to be stored as proper timestamps (were stored as numbers). | • Host: the date attributes listed above changed type. Re-sync to repopulate these records. |
| 5.3.38 | New Features - Added a TAGS attribute to the Vulnerability model. Qualys host-level tag names assigned to the host on which a vulnerability was detected are now mapped onto the finding, enabling tag-based filtering and reporting at the vulnerability level. Detection sync requests now include show_tags=1 so tag data is fetched automatically with no additional configuration. | N/A |
| 5.3.37 | Bug Fixes - Fixed a data integration failure on the Vulnerability Definition sync. The source severity score was being emitted as an Integer, but the platform schema requires a Double, causing the job to abort with an attribute type mismatch error. The value is now written as a Double, matching the type used by the sibling Vulnerability model. | N/A |
| 5.3.36 | Improvements Coding Standards Modernization - Bumped http-connectors-parent from 2.1.7 to 2.1.12 and connectors-model from 1.5.10 to 1.6.19 to align with the current connector framework baseline. - Replaced all new AttributeInfoBuilder(...) usages with AttributeInfos.newAttribute(...) across all model classes. This ensures custom attributes are registered with the correct consolidation priority, so they participate properly in attribute consolidation and value precedence. - Removed local addAttribute helper methods in favor of AttributeUtils.addAttribute from connectors-model, which prevents null values from silently reaching the attribute builder and adds type validation. - Migrated storage initialization from the deprecated LocalFactory / LocalConfig to StorageManager from connectors-model. - Removed the connector-local InstantDeserializer / InstantUtils in favor of OptionalInstantDeserializer from connectors-model, which supports a broader set of input formats. - Applied Spotless code formatting to the full codebase. - Restructured readme_vm.md to follow the new README standard with Functionality, Authentication, Configuration, per-model Attribute Mapping, Filters, Sync Duration Parameters, and Model Relationship Diagram sections, including documented Operation Options and complete attribute mapping tables for Host, Vulnerability, and Vulnerability Definition models. | N/A |
| 5.3.35 | No changes in this release. | N/A |
| 5.3.34 | No changes in this release. | N/A |
| 5.3.33 | Improvements - Cloud provider tags on the Host model are now recorded in a readable Key: <name>; Value: <value> format instead of the tag name alone, so the originating key and value are both visible. | • Host: cloud provider tag values changed format. Re-sync to repopulate this attribute. |
| 5.3.32 | No changes in this release. | N/A |
| 5.3.31 | No changes in this release. | N/A |
| 5.3.30 | New Features - Added NetBIOS hostname and DNS hostname attributes to the Host model, exposing the host name as reported by NetBIOS and by DNS separately. Bug Fixes - Hardened the Vulnerability Definition exploit and malware correlation parsing against missing nested elements, resolving a NullPointerException that could abort the sync when a definition had incomplete correlation data. | N/A |
| 5.3.29 | Bug Fixes - Host IP address attributes are now validated as real IP addresses before being stored, and public IP addresses are correctly mapped to the public IP attribute rather than the public DNS attribute. | N/A |
| 5.3.28 | No changes in this release. | N/A |
| 5.3.27 | No changes in this release. | N/A |
| 5.3.26 | New Features - Added an OS hostname attribute to the Host model. The OS-reported host name is also contributed to the host name identifiers used for asset correlation. | N/A |
| 5.3.25 | No changes in this release. | N/A |
| 5.3.24 | Improvements - The Vulnerability finding identifier now uses Qualys' native unique vulnerability ID when one is provided, falling back to the previous computed identifier only when it is absent. This produces more stable identifiers that match Qualys directly. | • Vulnerability: the finding identifier changed for detections that expose a native unique vulnerability ID. Re-sync to align existing findings with the new identifiers. |
| 5.3.23 | Improvements - The vulnerability detection source filter now accepts a free-form value, allowing detection results to be limited to specific Qualys detection sources rather than a simple on/off toggle. | N/A |
| 5.3.22 | No changes in this release. | N/A |
| 5.3.21 | No changes in this release. | N/A |
| 5.3.20 | No changes in this release. | N/A |
| 5.3.19 | No changes in this release. | N/A |
| 5.3.18 | New Features - Added Vulnerability detection sources and Latest vulnerability detection source attributes to the Vulnerability model and a corresponding sync option, so the scanner/agent source that detected each finding can be captured. | N/A |
| 5.3.17 | New Features - Added Agent activation key and Agent activation title attributes to the Host model, surfacing the Qualys Cloud Agent activation key and title assigned to each host. | N/A |
| 5.3.16 | No changes in this release. | N/A |
| 5.3.15 | No changes in this release. | N/A |
| 5.3.14 | Improvements - Upgraded to newer Qualys API versions for host listing, detection, and knowledge base retrieval. - Added Asset Risk Factor (ARF) filtering options, allowing detection results to be narrowed by ARF criteria. | N/A |
| 5.3.13 | No changes in this release. | N/A |
| 5.3.12 | No changes in this release. | N/A |
| 5.3.11 | No changes in this release. | N/A |
| 5.3.10 | Improvements - Renamed the Vulnerability Patch available attribute to Patchable for clarity and consistency. | • Vulnerability: the Patch available attribute was renamed to Patchable. Re-sync to repopulate findings under the new attribute. |
| 5.3.9 | Bug Fixes - The Qualys Detection Score (QDS) on the Vulnerability model is now stored as a numeric value, so it can be used in numeric comparisons and reporting. | N/A |
| 5.3.8 | No changes in this release. | N/A |
| 5.3.7 | No changes in this release. | N/A |
| 5.3.6 | Bug Fixes - Vulnerability Definitions with no reported supported modules are no longer dropped from the sync; only definitions exclusive to Web Application Scanning continue to be excluded. | N/A |
| 5.3.5 | New Features - Added a configurable request timeout setting, allowing the per-request HTTP timeout to be tuned for environments with large or slow Qualys responses. | N/A |
| 5.3.4 | Bug Fixes - The Host Asset ID attribute is now stored as text rather than a number, preventing precision loss and matching the identifier format returned by Qualys. | • Host: the Asset ID attribute type changed from number to text. Re-sync to repopulate this attribute. |
| 5.3.3 | No changes in this release. | N/A |
| 5.3.2 | New Features - Added lifecycle handling so that Host records not scanned within the last 30 days are retired automatically, and Vulnerability findings follow the lifecycle of their host. Improvements - Vulnerability findings now expose both a normalized status and the raw provider status, giving clearer visibility into the source detection state. | • Vulnerability: the source status attribute was split into a normalized status and a separate provider status. Re-sync to repopulate these attributes. |
| 5.3.1 | No changes in this release. | N/A |
| 5.3.0 | No changes in this release. | N/A |
| 5.2.4 | New Features - Added TruRisk scoring attributes ( TruRisk score, TruRisk score formula), an asset criticality score, agent status, and serial number to the Host model. Improvements - Reworked the Host and Vulnerability attribute model so attribute keys are stable internal identifiers with separate display titles, and broadened host correlation to use serial number and multi-valued host name, public IP, and public DNS identifiers. | • Host: host attribute identifiers and correlation keys changed. Re-sync to repopulate host records and re-resolve asset correlation. • Vulnerability: vulnerability attribute identifiers changed. Re-sync to repopulate findings. |
| 5.2.3 | New Features - Added Qualys Detection Score attributes ( QDS score, QDS severity, QDS factors) to the Vulnerability model, along with sync options to request QDS data and filter detections by QDS range. | N/A |
| 5.2.2 | Improvements - Renamed the Vulnerability Source severity attribute to Source severity score so the raw Qualys severity is clearly identified as a numeric score. | • Vulnerability: the Source severity attribute was renamed to Source severity score. Re-sync to repopulate findings under the new attribute. |
| 5.2.1 | Improvements - Renamed the Vulnerability detection Source severity attribute to Source severity score to clarify that it carries the raw numeric Qualys severity. | • Vulnerability: the Source severity attribute was renamed to Source severity score. Re-sync to repopulate findings under the new attribute. |
| 5.2.0 | No changes in this release. | N/A |
| 5.1.13 | No changes in this release. | N/A |
| 5.1.12 | Improvements - Vulnerability Definitions that apply only to Web Application Scanning are now excluded from the sync, reducing noise for vulnerability management deployments. | N/A |
| 5.1.11 | New Features - Added a Network ID attribute to the Host model, capturing the Qualys network a host belongs to. | N/A |
| 5.1.10 | No changes in this release. | N/A |
| 5.1.9 | No changes in this release. | N/A |
| 5.1.8 | Improvements - Added Asset Risk Score (ARS) sync options, allowing host results to be filtered by ARS range and to request ARS factor details. | N/A |
| 5.1.7 | No changes in this release. | N/A |
| 5.1.6 | No changes in this release. | N/A |
| 5.1.5 | Bug Fixes - Hardened CVSS v2 and v3 parsing on Vulnerability Definitions against malformed or missing vector strings, preventing sync failures on definitions with incomplete CVSS data. | N/A |
| 5.1.4 | Bug Fixes - CVSS vectors on Vulnerability Definitions are now parsed only when present, avoiding errors when a definition has no CVSS vector string. | N/A |
| 5.1.3 | No changes in this release. | N/A |
| 5.1.2 | No changes in this release. | N/A |
| 5.1.1 | No changes in this release. | N/A |
| 5.1.0 | New Features - Added a configurable maximum retry count for Qualys API requests, giving control over how aggressively transient failures are retried. Improvements - Hardened XML parsing by disabling external DTD loading and external entity resolution, addressing XML external entity (XXE) exposure when processing Qualys responses. | N/A |
| 5.0.18 | New Features - Added a Severity score attribute to the Vulnerability model alongside the normalized severity. Improvements - Refined vulnerability severity normalization so the displayed severity and its numeric score are derived consistently from the raw Qualys severity. | • Vulnerability: severity values were re-derived. Re-sync to repopulate the severity and severity score attributes. |
| 5.0.17 | Improvements - Vulnerability severity is now normalized to a standard scale, and the original Qualys severity is preserved separately as the source severity. | • Vulnerability: the severity attribute now carries a normalized value. Re-sync to repopulate findings with the normalized severity. |
| 5.0.16 | No changes in this release. | N/A |
| 5.0.15 | No changes in this release. | N/A |
| 5.0.14 | Improvements - Added a stable unique identifier and used it for asset/finding correlation across the Host, Vulnerability, and Vulnerability Definition models. | N/A |
| 5.0.13 | Improvements - Renamed the Vulnerability Definition Category attribute to Categories to support multiple category values. | • Vulnerability Definition: the Category attribute was renamed to Categories. Re-sync to repopulate definitions under the new attribute. |
| 5.0.12 | Improvements - Renamed the Host Category attribute to Categories and made it multi-valued, so cloud hosts are now tagged as both a host and a virtual machine. | • Host: the Category attribute was renamed to Categories and is now multi-valued. Re-sync to repopulate host records under the new attribute. |
| 5.0.11 | New Features - Added asset risk and criticality scores, ARS formula, owner, tracking method, tags, last authenticated scan time, first seen time, and Google Cloud (GCP) instance attributes to the Host model. | N/A |
| 5.0.10 | Improvements - Reworked Host network attributes to separate public and private addressing: DNS and IP attributes were renamed and split into public/private variants, NetBIOS was folded into host name, and host correlation now keys on the public DNS name and public IP address. | • Host: network attribute identifiers and correlation keys changed. Re-sync to repopulate host records and re-resolve asset correlation. |
| 5.0.9 | No changes in this release. | N/A |
| 5.0.8 | No changes in this release. | N/A |
| 5.0.7 | New Features - Added Hostname and Instance ID attributes to the Host model, populated from cloud (EC2/Azure) instance metadata. Improvements - Updated host correlation to key on MAC addresses, instance ID, and host name, improving matching for cloud-hosted assets. | • Host: host correlation identifiers changed. Re-sync to re-resolve asset correlation. |
| 5.0.6 | No changes in this release. | N/A |
| 5.0.5 | Improvements - Added explicit identifier mappings for asset and finding resolution across the Host, Vulnerability, and Vulnerability Definition models, improving how records are correlated and deduplicated. | N/A |
| 5.0.4 | Improvements - Restored the Vulnerability Definition model (model type VulnerabilityDefinition), reverting the temporary switch to a generic Finding Definition. | • Vulnerability Definition: the model type was changed back from FindingDefinition to VulnerabilityDefinition. Purge and re-sync vulnerability definitions if they were synced under the interim type. |
| 5.0.3 | No changes in this release. | N/A |
| 5.0.2 | Improvements - Switched the vulnerability definition model to a generic Finding Definition type (model type FindingDefinition). | • Vulnerability Definition: the model type changed from VulnerabilityDefinition to FindingDefinition. Purge and re-sync vulnerability definitions. |
| 5.0.1 | Improvements - Split the Vulnerability CVE attribute into CVE IDs and CVE records, and renamed the Last updated attribute to Source last modified on the Vulnerability and Vulnerability Definition models. The legacy Times found attribute was removed. | • Vulnerability, Vulnerability Definition: CVE and date attribute identifiers changed. Re-sync to repopulate these records under the new attributes. |
| 5.0.0 | Overview The Qualys Vulnerability Management connector integrates with Qualys VM to synchronize scanned hosts, detected vulnerabilities, and the underlying vulnerability definitions from the Qualys KnowledgeBase. Category: Vulnerability Management Models | N/A |